
See a feature in an app and wonder how it works? Until recently, answering that question meant weeks of expert work with tools like Ghidra or IDA Pro. REA (Reverse Engineer Anything) changes the equation: it connects your AI coding agent to professional reverse engineering tools through a single MCP server, letting you investigate any app — from its visible behavior down to native binaries — by simply asking. With over 265,000 GitHub stars as of October 2026, it is one of the most significant open-source AI developer tools of the year. Here is what it does, how it works, and how to use it responsibly.
What is REA?
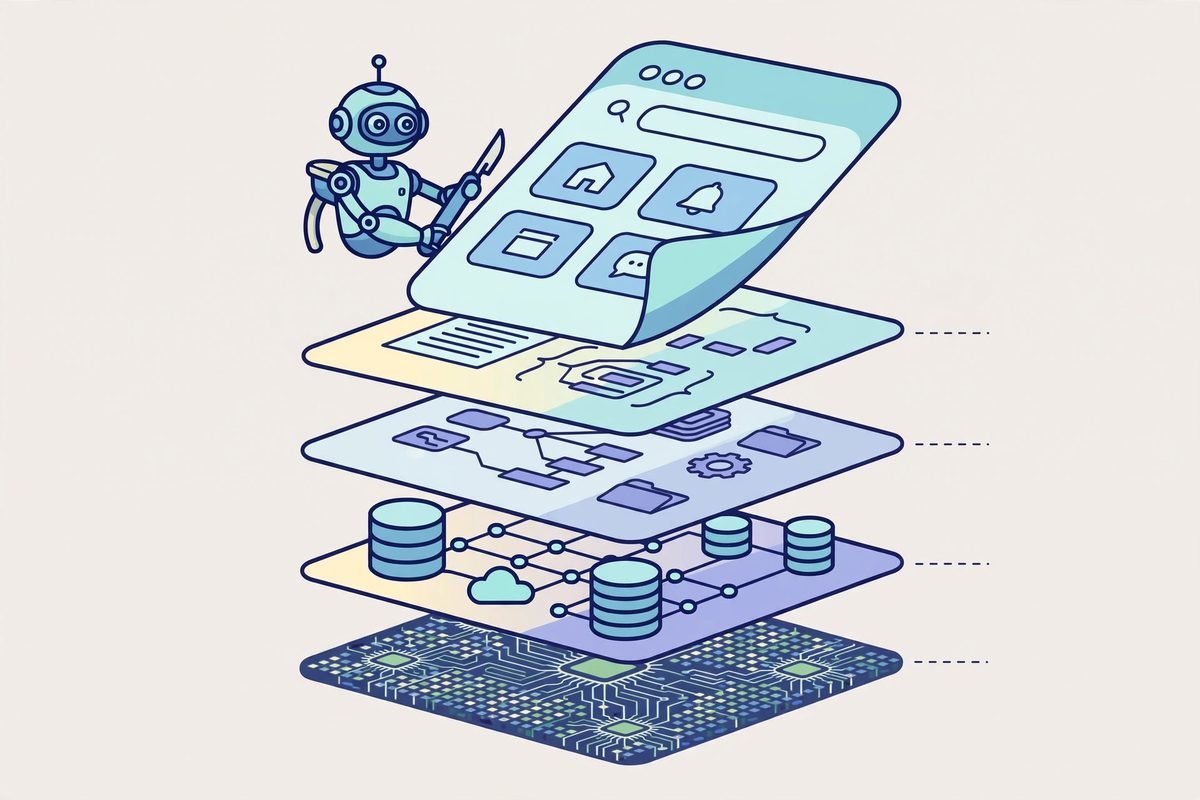
REA, by morluto, describes itself in one line: “Reverse engineer anything with agents, from app behavior down to native binaries.” Technically, it is one MCP (Model Context Protocol) server for reverse engineering across binaries, applications, and runtime behavior. Instead of learning five different specialized tools, you ask your AI agent — in plain language — to investigate a piece of software, and REA routes the work to the right underlying engine.
The project’s own pitch captures the core use case: see a feature you like, understand how it works down to the binary level. Your agent can inspect an app without its source code, explain how a feature works, show the evidence behind its conclusions, and even build a version of that feature for your own project.
The numbers tell you this is not a niche experiment: the repository holds over 265,000 stars and 66,000 forks on GitHub, is written in TypeScript, ships under the business-friendly MIT license, and was first released in April 2026. It also maintains an official site at rea.tools with illustrated guides, real case studies, and an active Discord community.
What REA can analyze
REA connects your agent to tooling for four kinds of targets:
- Native binaries — compiled executables analyzed through professional engines. REA can work with an existing Hopper, Ghidra, or IDA installation, and setup can optionally install Hopper with your approval.
- JavaScript and Electron apps — static analysis of extracted app directories or ASAR archives, mapping modules, imports, and Electron boundaries. No native analysis engine required for this.
- .NET assemblies — inspection of managed .NET code.
- Websites — analysis of web application behavior and structure.
Two design decisions stand out. First, analysis runs locally — your target software is not uploaded to a cloud service, which matters enormously when you are investigating proprietary or sensitive binaries. Second, results include the evidence and limitations behind each conclusion. That is the right design for a field where a confident-but-wrong answer is worse than no answer.
How REA works
Setup is a single command with Node.js and npm installed:
npx rea-agents setup
You choose your agents, review the proposed configuration changes, and approve them. Setup registers REA’s MCP server with your agent and installs matching workflow instructions (backing up your existing configuration first), then you restart the agent. Supported agents include Claude Code, Codex, Cursor, Gemini CLI, and Grok Build, among others.
After that, you just ask. The project’s own example: “Understand how search works in the Notes app, show me the evidence, and build a similar feature for my project.” Replace “Notes” with your target and “search” with the feature you want to understand.
Prefer the terminal? The same tools work directly, for example analyzing an extracted Electron app:
npx -y rea-agents@latest analyze-javascript-application /absolute/path/to/app --json
For regular use you can install the global command with npm install --global rea-agents and run rea --help. Full documentation, including manual MCP registration and provider configuration, lives in the repo’s docs folder and on rea.tools.
Why REA is trending
Reverse engineering has always been a high-skill discipline. Tools like Ghidra (free, from the NSA) and Hopper are powerful but demand serious expertise — reading assembly, understanding calling conventions, and navigating enormous control-flow graphs. That expertise bottleneck is exactly what REA attacks: the agent does the tedious traversal and correlation, while the human directs the investigation and judges the evidence.
The timing matters too. AI coding agents went mainstream in 2025–2026, and MCP became the standard way to give them new capabilities. REA sits precisely at that intersection: it turns the agent you already use for writing code into an analyst that can also read code nobody wrote down — compiled, minified, or obfuscated. For security teams, that means faster triage. For product teams, it means understanding competitors’ implementations. For developers, it means learning from software the way you would from open source, even when the source is not open.
From our experience: what changes when agents can reverse engineer
We have worked with Ghidra and Hopper directly while building security tooling, so we have felt the traditional pain: even a simple question — “where does this app validate the license key?” — can mean days of staring at disassembly. An agent that can drive those same tools changes the economics of the investigation, not just its speed. A security audit that was previously out of budget becomes feasible. A suspicious binary can get a first-pass triage in an afternoon instead of a sprint.
But two cautions from experience. First, agent output in reverse engineering must be verified — REA’s evidence-and-limitations design shows its authors understand this, but the human still needs to check critical conclusions against the actual disassembly before acting on them. Second, the tool does not replace RE fundamentals: the teams getting the most from REA will be the ones who can tell when the agent’s reasoning about a binary is wrong. Use it as a force multiplier for expertise, not a substitute for it.
Use it responsibly: the legal and ethical boundaries
Powerful tools come with boundaries, and reverse engineering is no exception. Legitimate uses include security research (analyzing malware, auditing software you depend on), interoperability (understanding file formats and protocols), competitive feature research (learning how a feature works to build your own original implementation), and education.
The rules are straightforward: only analyze software you have a legal right to investigate — your own systems, software you are licensed to test, or targets covered by a bug bounty or engagement scope. Respect license agreements and terms of service, which in some jurisdictions restrict reverse engineering. Never use REA output to steal proprietary code verbatim, bypass licensing or DRM, or attack systems you do not own. When in doubt, get written authorization first — it is the same standard professional security researchers work under.
One more practical note from the project’s own README: get REA only from official sources — the morluto/rea repository, rea.tools, or the rea-agents npm package. A trending project attracts copycats, and a similar repository name does not establish that a download is legitimate.
Getting started with REA
- Prerequisites: Node.js and npm installed. For native binary analysis, an existing Hopper, Ghidra, or IDA installation helps (setup can optionally install Hopper with your approval).
- Install: run
npx rea-agents setup, choose your agents, review and approve the proposed changes, then restart your agent. - First investigation: pick a target you own, ask your agent to explain one specific feature, and demand the evidence — practice judging the agent’s conclusions before trusting them on anything important.
- Go deeper: the guides on rea.tools walk through real investigations, and the repo docs cover manual MCP registration and advanced configuration.
Frequently asked questions
What is REA (morluto/rea)?
REA — “Reverse Engineer Anything” — is an open-source MCP server that connects AI coding agents (Claude Code, Codex, Cursor, and others) to professional reverse engineering tools, so you can investigate apps from their behavior down to native binaries by asking questions in plain language.
Is REA free to use?
Yes. REA is open source under the MIT license, which means you can use it commercially at no cost. You will need your own AI agent subscription (Claude Code, Cursor, etc.), and optionally a native analysis engine like Hopper, Ghidra, or IDA for binary work.
Do I need to know reverse engineering to use REA?
You can start without deep RE knowledge — the agent drives the tools. But you will get far better (and safer) results if you can sanity-check its conclusions. Treat it as a force multiplier for learning and investigation, and build your fundamentals as you go.
Is reverse engineering with REA legal?
It depends on what you analyze and where you are. Security research, interoperability work, and analyzing your own systems are widely legitimate; license agreements and local laws can restrict it in other cases. Only investigate software you have the right to test, and get written authorization when in doubt.
Where can I find more trending open-source AI tools?
We track them on our Trending GitHub AI Repos page and in the AI Tools Directory — including our roundup of 10 open-source AI tools trending on GitHub.
REA is the kind of infrastructure shift that quietly rewrites what small teams can do — security analysis that used to need a specialist is now a conversation with your agent. If you want help putting AI-assisted analysis into your security workflow, or building on open AI infrastructure in general, talk to our team.